Early bird until
2 days / In-person technical training
Breaking BitLocker
From an encrypted notebook to a working recovery password.
Build the hardware skills to break TPM-only BitLocker protection. In two days of guided practical work, follow the path from opening a supplied notebook to recovering its BitLocker recovery password and accessing its data. Take the target notebook and lab equipment home with you.
What you take away
Learn the complete recovery workflow
When an encrypted notebook arrives on your desk, you need to know whether a practical route to its data exists. That means assessing the target, making reliable measurements and turning recovered key material into a usable result.
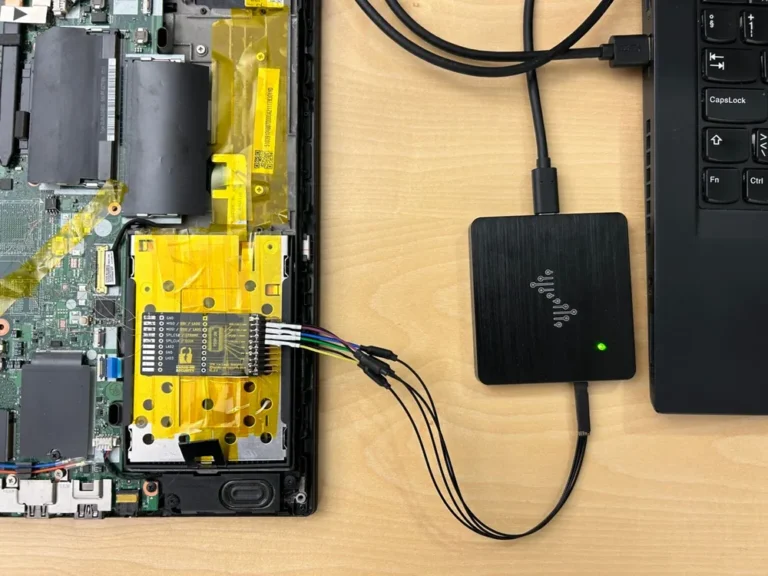
Breaking BitLocker teaches that process on real hardware. You assemble adapters, inspect a notebook, capture TPM communication and use the recovered key material to unlock the training target. Focused explanations introduce each stage, followed by guided practical work with your trainers.
What you will be able to do
- Assess the hardware and protection settings that determine which BitLocker recovery approaches are applicable.
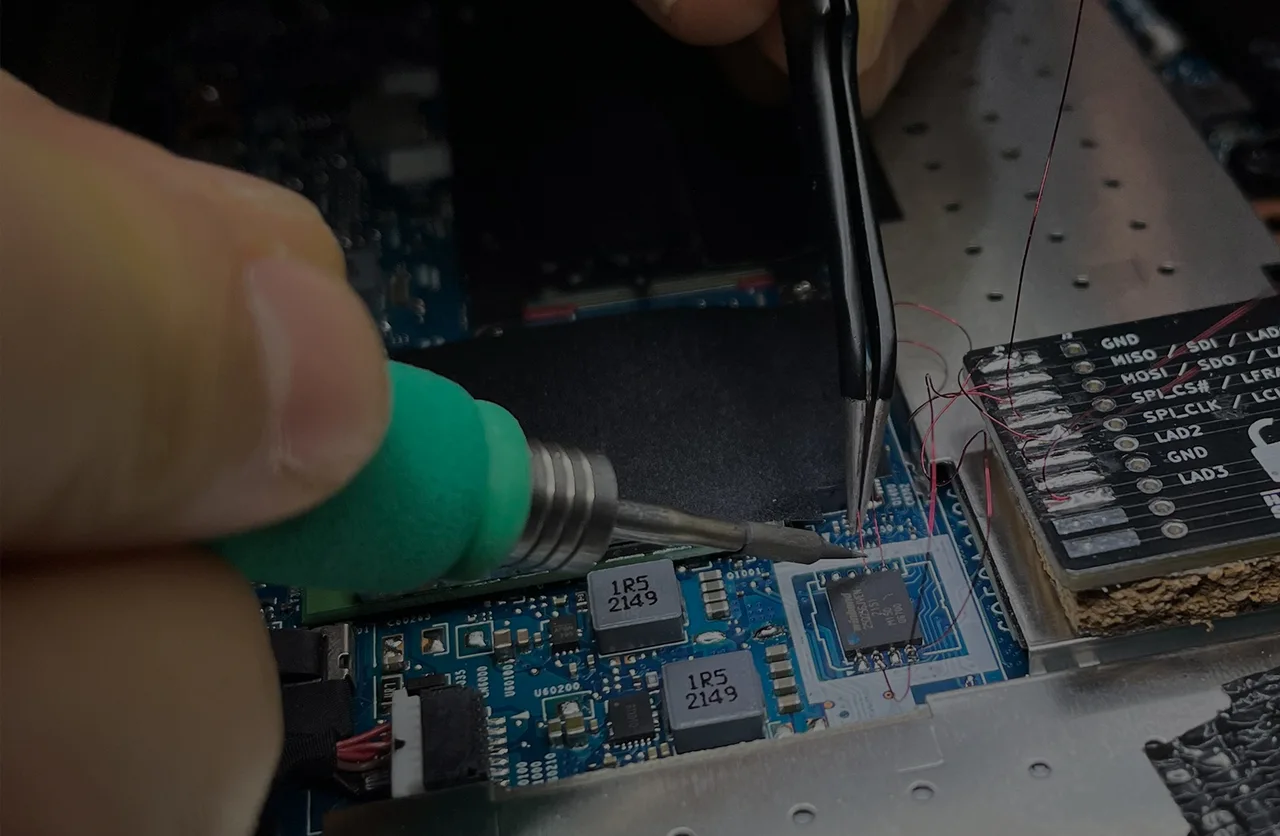
- Disassemble a notebook, identify relevant components and make the solder connections needed for the hardware labs.
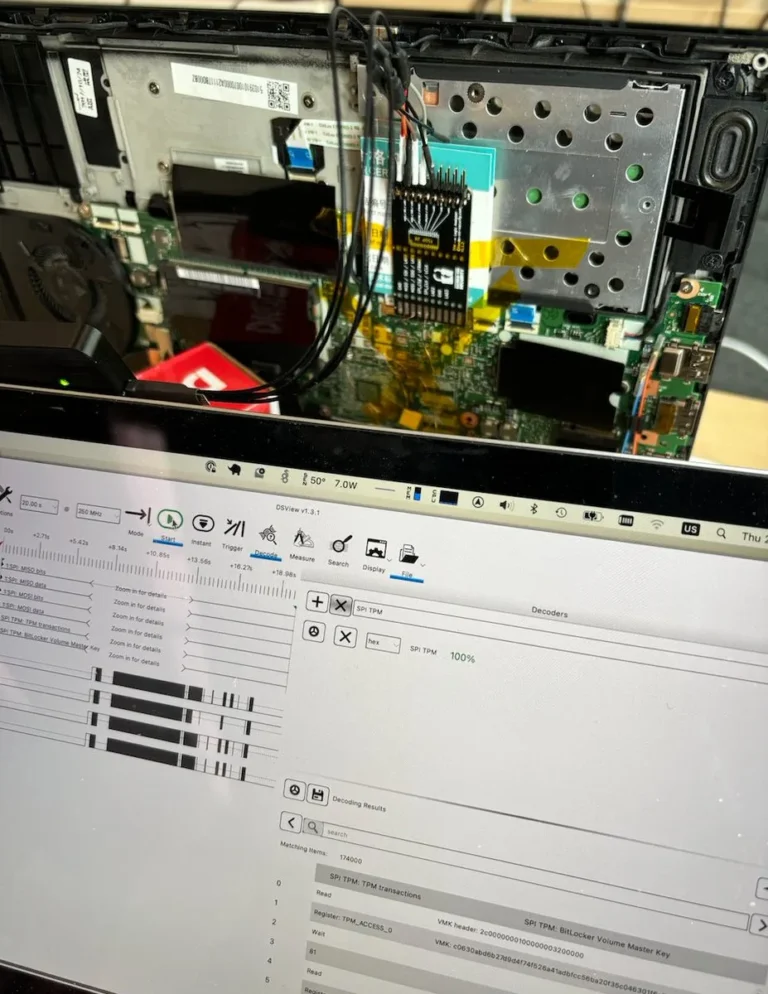
- Capture and interpret TPM bus traffic with a logic analyzer.
- Recover the training target’s BitLocker recovery password and access its data for forensic examination.
Understand what makes an attack work
The central hardware workflow targets suitable TPM-only BitLocker configurations with a discrete TPM. The training also covers boot-chain and memory-based approaches. Applicability depends on the device, firmware, Windows state and protection settings; understanding those conditions is part of the skill you take away.
Day 1 · Build your skills and prepare the target
Get familiar with your new equipment and learn the basics of soldering through guided practice. Then explore BitLocker’s protection model and how it relates to practical recovery techniques. You will work through the BitPixie/YellowKey lab and open the supplied notebook to investigate its hardware.
- Build adapters and practise soldering before working on the target.
- Understand BitLocker key protectors, the boot process and the conditions behind the BitPixie/YellowKey lab.
- Inspect notebook internals, use component documentation and prepare for forensic acquisition.
Day 2 · Capture the key and complete the recovery
Begin with a demonstration of DMA and memory analysis using PCILeech and MemProcFS. Then connect to the target’s TPM bus, capture and decode its communication, and follow the recovered key material through to a usable recovery password.
- Identify the TPM, understand LPC/SPI communication and connect your adapter.
- Practise logic-analyzer capture, decoding and troubleshooting.
- Unlock the training volume and extract artifacts for forensic examination.
Included, not borrowed
Keep practising with your own equipment
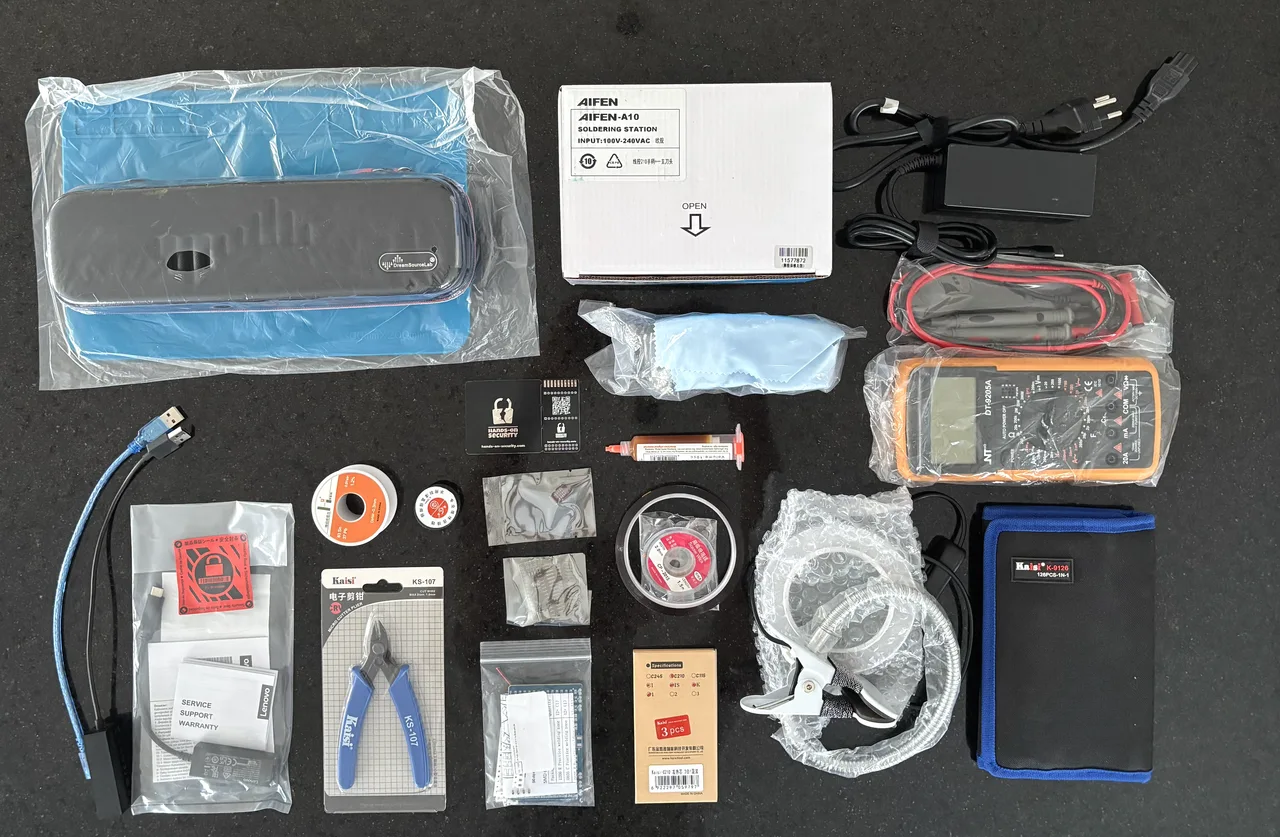
Your work does not end when the training does. Keep the supplied target notebook and lab kit so you can repeat the exercises, develop your technique and share what you have learned with your team.
- Off-the-shelf notebook, yours to keep
- High-performance logic analyzer
- Custom TPM adapters, probes and wiring accessories
- Soldering equipment, including the soldering station for our Zürich training
- Training slides, recovery scripts and test data
The class page lists the exact inclusions for your chosen date.
View class & registerIs this for you?
Designed for technical practitioners
This training is particularly relevant to digital forensics practitioners who need to assess recovery options on encrypted devices, and penetration testers who need to demonstrate the impact of physical access. Security researchers and endpoint engineers will also gain practical insight into how hardware, boot state and configuration affect protection.
Prerequisites & preparation
No soldering experience required
You do not need previous micro-soldering experience. We teach the techniques and guide the practical work. You should be comfortable with operating systems, a terminal and technical troubleshooting, and willing to work carefully on real hardware.
Bring an analysis laptop with administrator or root access, permission to install tools, USB 3.0 connectivity and the ability to run the required virtual machine and analysis software. We supply the target notebook. Check the preparation requirements for your chosen class.
Unsure about training fit or your setup? Ask the trainers before registering.
A practical capability for your team
Build the ability to assess physical-access risk, investigate encrypted endpoints and explain findings with evidence from practical work. The take-home equipment gives your team a basis for continued testing, internal demonstrations and knowledge sharing.
Your instructors
Meet your trainers.
Practical guidance throughout the class.
Engineering / Digital forensics
Pascal Gujer
Pascal combines a background in electrical engineering with an MSc in Advanced Cyber Security and Digital Forensics. His master’s research explored vulnerabilities in Microsoft’s BitLocker implementation.
He approaches security research from an engineering perspective: questioning design assumptions, reverse-engineering implementations, and turning complex vulnerabilities into practical, reproducible attacks.
Digital forensics / Hardware
Joel Frei
Joel works across digital forensics, from mobile devices and storage media to embedded systems and complex hardware investigations.
His practical experience with flash memory and micro-soldering connects forensic questions with the physical work required to investigate real devices.
Black Hat USATwo classes / 28 students in 2023
4.8 / 52023 participant feedback, with Popp Schweiz AG
100+Practitioners trained over the life of the training
Taught at Black Hat USA and independently in Zürich. You may also know this training as Breaking BitLocker. The syllabus continues to evolve with hardware, Windows and research. Black Hat USA 2023 listing (PDF).
Previous classes
What participants say.
Some participants work in law enforcement or other sensitive roles and prefer not to be named. Alongside their anonymous feedback, others have shared their experience publicly.
Public reviews
“Very impressive training, the right mix between theory and practical work.”

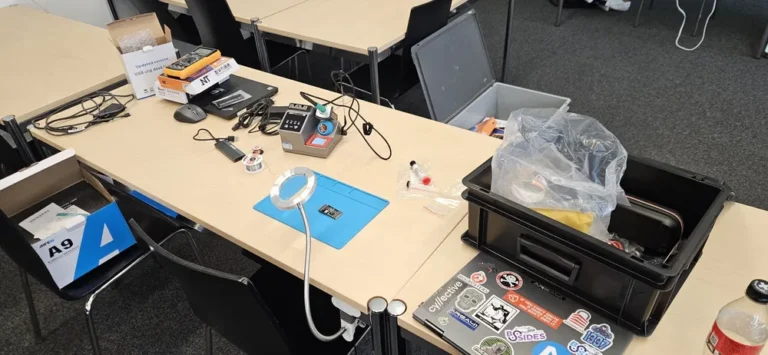
“The cherry on top: the course included a hardware kit containing all necessary tools to perform the attack.”
“The training was excellent and got us really excited about the topic.”
More public feedback
“Thanks a lot for your training, you guys rock!”
“thanks #handsonsecurity for the amazing training”
From feedback forms & email
“Very smooth experience, especially considering the complexity of the topic. Well-paced.”
“Individual help to participants from the trainers was awesome.”
“That was 1 great class. Thank you!”
Selected participant feedback from previous training editions.
Before you book
Questions, answered.
Is this a demonstration or a practical class?
You work on supplied training hardware yourself. The training combines explanation, guided practical exercises and discussion of the defensive implications.
Do I need to know how to solder?
No. We introduce the relevant techniques and guide you through the practical work. A willingness to work carefully on real hardware matters more than prior soldering experience.
What do I keep?
You keep the relevant training hardware and target notebook. The exact kit evolves, so check the inclusions on the class page for your chosen date.
Does every technique work on every BitLocker system?
No. Hardware, firmware, operating-system state and protection settings matter. Understanding those conditions and their defensive implications is a central part of the training.
Is this training also called Breaking BitLocker?
Yes. Breaking BitLocker is the short training name used on our flyers and class listings. The training has been taught at Black Hat USA and in Zürich, and the syllabus continues to evolve.
Can my organization book a private class?
Yes, by arrangement. Contact us with your team size, technical objectives, location and preferred timing.
How do registration and payment work?
Select a class and complete its registration form. We check availability and send an invoice for bank transfer. Registration is binding under the training terms; your place is confirmed after payment confirmation.
Train with us
Bring the skills back to your lab
Choose a class to see dates, pricing, equipment inclusions and registration details.
Early bird until
From the workbench
A short lab preview.
See our 60-second TPM sniffing preview on YouTube. The January class dates mentioned in the video are historical; current dates are listed above.
Watch the lab preview